It was a busy week at VMware Explore last week, but we still managed to record new content to discuss what was happening at VMware Explore. We spoke with folks like Kit Colbert, Chris Wolf, Dave Morera, Sazzala Reddy, and many others. We also recorded episodes to cover the vSAN 8.0 and vSphere 8.0 release. For vSAN 8.0 we asked Pete Koehler to go over all the changes with vSAN Express Storage Architecture. vSphere 8.0 was covered by Feidhlim O’Leary, going into every aspect of the release, and it is a lot.
vSphere
Introducing vSphere+ and vSAN+
VMware just announced vSphere+ and vSAN+ today. I was reading up on the offering and personally was very intrigued about it. I have to be fair, at first I was under the impression that vSphere+ and vSAN+ was only about subscription-based licensing, but it is not, it is much more than that. If you like to head more about it, Frank and I invited Himanshu Singh to the podcast to provide us a quick overview, in ~20 minutes you know everything you need to know at this stage, make sure to listen to it below or open up the podcast in your favorite podcast app.
I am not going to type up a summary of the podcast, but I do briefly want to share my thoughts. First of all, as mentioned already, vSphere+ aka Project Arctic is about much more than just subscription-based licensing. Yes, the platform is subscription-based, but it also delivers additional capabilities to your on-prem environment. Details of pricing and packaging is still to be announced, but Himanshu mentioned to us that VMware will provide an upgrade path from perpetual licenses to vSphere+ taking into account that you have already bought licenses. Mind, most of you renew SnS every X years, this would be also included in vSphere+. But that is not what excited me, what excited me is that you get access to the Cloud Console, which basically provides a holistic overview of your VMware estate, with today a focus on vSphere and vSAN, and the extra capabilities the platform provides.
This Cloud Console is, no surprise I guess, running in the cloud and connects your on-prem VMware environment to cloud services. In order to do so, you will need to deploy a Cloud Gateway and connect your vCenter Server instances to the gateway, do note that each Cloud Gateway in the initial release can manage up to 4 vCenter Server instances. You can, however, deploy multiple Cloud Gateway of course if you want to manage more vCenter Server instances.
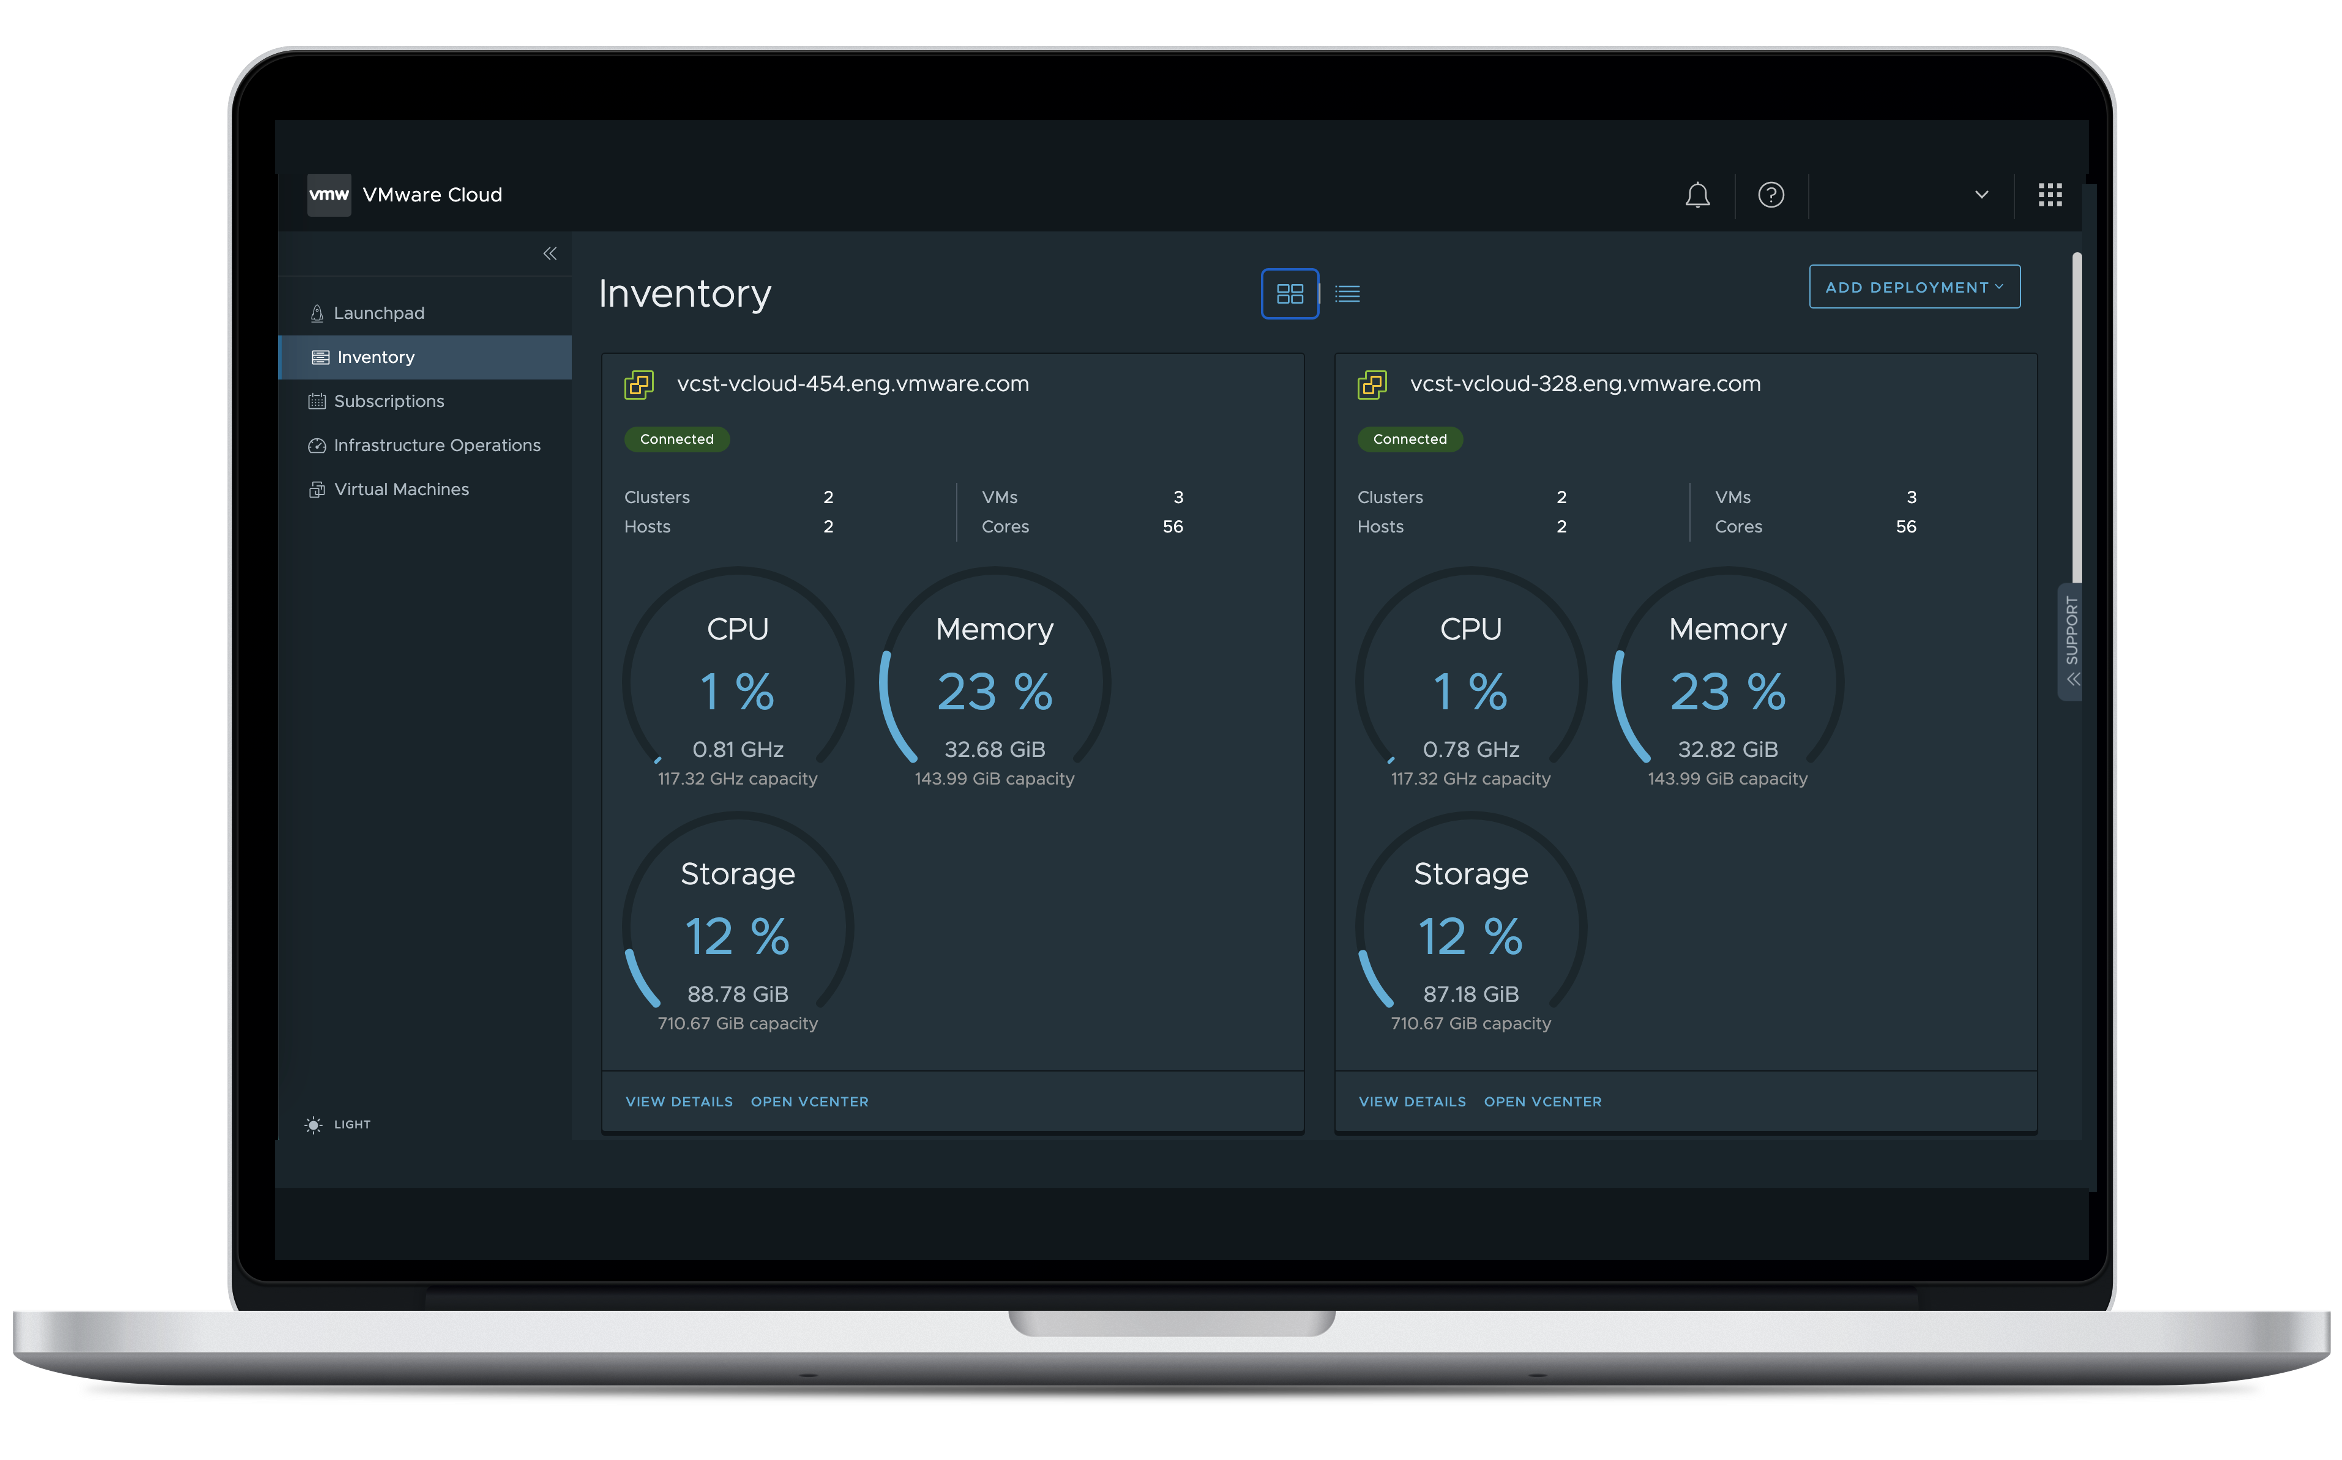
Now, when you get access to the Cloud Console, it immediately shows you what the value is, you will get an instant overview of all resources available in your VMware environment. Not only that, but you will also get centralized alerts and events, a global inventory, VM provisioning capabilities, and enhanced vCenter upgrade capabilities, which is my favorite feature! This upgrade capability is very useful as it shortens the downtime/maintenance window for vCenter to roughly 5 minutes. It also provides the ability to do a rollback if needed. There’s much more, but I will leave that for a follow up podcast with one of the vSphere+ specialists!
The two last things I want to point out is the fact that additional services will also be provided through this platform. There are the Developer Services and there are Add-On Services. The Developer Services are included, the Add-On services are not included in the price, but are fully integrated and can be subscribed to individually. A great example of an add-on service is VMware Disaster Recovery as a Service solution. Of course, developer services is all about Kubernetes as it includes Tanzu Standard Runtime, and Tanzu Mission Control Essentials!
Hopefully this provides a decent enough overview of what vSphere+ is. Make sure to listen to the podcast episode, it is only ~20 minutes and it provides a bit more background and detail!
Nested Fault Domains on a 2-Node vSAN Stretched Cluster, is it supported?
I spotted a question this week on VMTN, the question was fairly basic, are nested fault domains supported on a 2-node vSAN Stretched Cluster? It sounds basic, but unfortunately, it is not documented anywhere, probably because stretched 2-node configurations are not very common. For those who don’t know, with a nested fault domain on a two-node cluster you basically provide an additional layer of resiliency by replicating an object within a host as well. A VM Storage Policy for a configuration like that will look as follows.
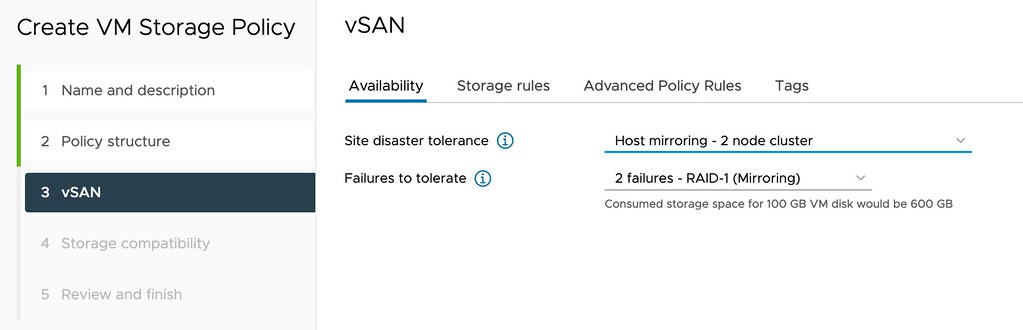
This however does mean that you would need to have a minimum of 3 fault domains within your host as well if you want to, this means that you will need to have a minimum of 3 disk groups in each of the two hosts as well. Or better said, when you configure Host Mirroring and then select the second option failures to tolerate the following list will show you the number of disk groups per host you need at a minimum:
- Host Mirroring – 2 Node Cluster
- No Data Redundancy – 1 disk group
- 1 Failure – RAID1 – 3 disk groups
- 1 Failure – RAID5 – 4 disk groups
- 2 Failures – RAID1 – 5 disk groups
- 2 Failures – RAID6 – 6 disk groups
- 3 Failures – RAID1 – 7 disk groups
If you look at the list, you can imagine that if you need additional resiliency it will definitely come at a cost. But anyway, back to the question, is it supported when your 2-node configuration happens to be stretched across locations, and the answer is yes, VMware supports this.
Does the Native Key Provider require a host to have a TPM?
I got this question on the VMTN forum this week, does the Native Key Provider require a host to have a TPM? (Trusted Platform Module) The documentation does discuss the use of TPM 2.0 when you enable the Native Key Provider. Let’s be clear, the vCenter Server Native Key Provider does not require a TPM! If a TPM is available on each host then it will be used by the Native Key Provider to store a secret on, which enables us to encrypt and decrypt the ESXi configuration. Again, as stated, it is not a requirement to use a TPM. I have asked to get the documentation appended so that it is officially documented as well, just posting it here so that it indexed by google.
Unexplored Territory #010: Terraform and declarative automation with Kyle Ruddy
In episode #010 of the Unexplored Territory Podcast we talk to Kyle Ruddy, Tech Marketing guru at Hashicorp. Kyle explains how Hashicorp got started, what the difference is between imperative and declarative automation, and why Terraform (and other Hashicorp products/services) should be included in every multi-cloud architecture. Listen now via Apple (https://apple.co/34H5OcV), Spotify (https://spoti.fi/3J5MPrl), any other podcast app of your choice, or simply use the embedded player below!